
For digital agencies, managed service providers (MSPs), and web development studios, few operational failures are as damaging, or as preventable, as an accidental asset expiration. When a client’s primary domain, SSL certificate, or DNS hosting lapses, the consequences show up quickly: websites go offline, email routing breaks, checkout flows halt, and client trust erodes.
Yet in many agencies, renewal management remains reactive. Account managers rely on scattered calendar reminders, shared spreadsheets updated sporadically, or automated notices sent to an inbox no one monitors. When an emergency strikes, the team scrambles to find registrar credentials, track down an approver, and replace an expired credit card before the domain slides into a costly recovery window.
Moving from firefighting to predictable operations does not require enterprise bureaucracy. It requires a disciplined weekly rhythm, clear data hygiene rules, and standardized handoffs. This guide lays out an operational blueprint for client renewal workflows, updated for the 2026 landscape of RDAP, shorter certificate lifetimes, and the lifecycle rules that govern what happens when a domain lapses.
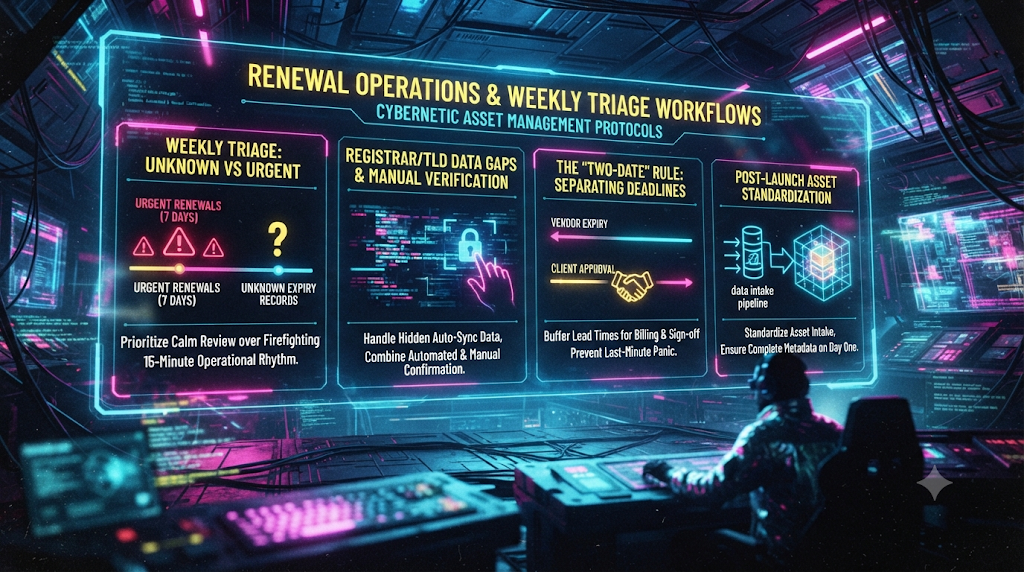
1. Running a 15-Minute Weekly Renewal Triage: Prioritizing “Unknown” vs. “Urgent” Client Assets
Most agencies treat renewals like an emergency room: whatever is bleeding loudest gets attention. In renewal operations, that usually means an asset expiring in the next 48 to 72 hours. Urgent expirations obviously demand action, but focusing only on imminent deadlines creates a blind spot that guarantees future emergencies.
To break the cycle, operations leads and account managers can run a 15-minute weekly renewal triage at the same time every week. A mid-week slot (Tuesday or Wednesday) is a practical choice: it avoids Monday inbox overload and leaves several working days to contact registrars or chase client billing approvals before the weekend.
Why “Unknown Expiry” Records Are a Hidden Trap
When auditing a typical agency asset tracker, records fall into three buckets:
- Healthy: expiring in more than 45 days, with a verified date.
- Approaching: expiring within 45 days.
- Unknown: missing expiration dates, unverified ownership, or failed lookups.
The trap is treating “Unknown” as “Low Priority.” An asset with no known expiration date is not safe; it is an unmeasured risk. An unknown status usually points to one of three underlying issues:
- A failed or unsupported lookup: The tracking tool could not retrieve or parse the registry’s public record (common for some country-code domains, covered in Section 2).
- Fragmented custody: The client registered the domain under a personal account or a former freelancer’s email, leaving the agency without visibility.
- A lapse that no alert will catch: The asset could be expiring tomorrow, and no countdown exists because the system has no baseline date.
If your weekly triage only reviews assets expiring in the next 7 to 14 days, Unknown records can sit untouched for months, until the day the client calls asking why the website is down.
The 15-Minute Triage Agenda
A strict timebox keeps the meeting from turning into a sprawling status call. Use a simple three-tier framework:
| Priority Tier | Timeframe / Status | Operational Goal | Required Action |
|---|---|---|---|
| Tier 1: Critical | Expiring in 0–14 days | Prevent service interruption | Verify auto-renew status, confirm the payment method is valid, or renew manually right away. |
| Tier 2: Discovery | Status Unknown or lookup error | Eliminate blind spots | Investigate up to 3 unknown records per week by logging into the registrar or asking the client to verify. |
| Tier 3: Pipeline | Expiring in 15–45 days | Secure client sign-off | Send approval requests, confirm who pays, and confirm registrar login access. |
Minutes 1–5: Clear Tier 1. Review every domain, SSL certificate, hosting plan, and software license expiring within 14 days. Do not assume “Auto-Renew: On” guarantees safety. Confirm that the card on file has not expired and that the client has approved the charge.
Minutes 6–10: Shrink Tier 2. Pick the three most client-critical assets lacking a verified expiration date. Assign an owner to check the registrar or DNS provider, or email the client’s IT contact, to establish a confirmed date. Resolving three unknowns a week clears roughly 150 records over a year.
Minutes 11–15: Advance Tier 3. Look at assets approaching their internal approval deadlines over the next two weeks, and send templated client check-ins so approvals are secured long before the asset reaches Tier 1.
2. When a TLD or Registrar Hides Expiry Data: Building a Manual Verification Habit
Many agencies rely on monitoring tools that query public registration databases for expiration dates, nameservers, and registrar details. Automation often hits a wall because of privacy rules and registry-level differences.
Why Automated Lookups Fail
The EU’s General Data Protection Regulation (GDPR) took effect in 2018, and ICANN responded with its Temporary Specification for gTLD Registration Data, which led to widespread redaction of personal data in public WHOIS records. That interim regime was replaced by ICANN’s Registration Data Policy, which took effect on August 21, 2025.
Alongside the privacy changes, the lookup protocol itself changed. ICANN’s gTLD registry and registrar obligations to run WHOIS (port 43 and web-based WHOIS) sunset on January 28, 2025, making the Registration Data Access Protocol (RDAP) the definitive source for generic TLD registration data. RDAP returns structured JSON, with the expiration date delivered as a standard event rather than a free-text field. Some registries and registrars continue to run WHOIS voluntarily, so port 43 does not disappear everywhere at once, but tools built only on legacy WHOIS parsing are increasingly fragile.
For generic TLDs such as .com, .net, and .org, the expiration date remains a mandatory part of the public RDAP record. The visibility problem is concentrated elsewhere:
- Country-code TLDs (ccTLDs): These registries are not bound by ICANN’s gTLD contracts and set their own data policies and technical rollouts. Some do not publish an expiry date in public lookups at all. For example,
.de(DENIC),.eu(EURid), and.ch/.li(SWITCH) do not expose the date to anonymous queries; the registrar is the source of truth. ccTLD RDAP coverage is also uneven, with.deand.eustill relying on legacy WHOIS rather than RDAP. - Registry date vs. registrar reality: For gTLDs, the public date is the registry’s expiration date. During the post-expiration auto-renew grace period, that date can appear extended even though the registrar has not been paid and may delete the domain if no one renews it. A “future” date in a public lookup is not proof that the client’s renewal is paid.
- Non-domain assets: SaaS subscriptions, plugin licenses, and API tokens have no public lookup protocol at all. Public SSL certificates are a partial exception, since the expiry date can be read from the certificate a site serves, but private or internal certificates and certificates behind a firewall cannot be checked that way.
When a tool encounters a ccTLD with no public expiry date or a rate-limited endpoint, it typically returns “Unknown,” “N/A,” or a stale cached value.
Pairing Automation with Structured Manual Verification
Relying solely on automated lookups creates false confidence. Pair automated RDAP checks with a manual verification habit for restricted TLDs and non-public assets:
- Tag restricted TLDs at intake. Maintain an internal list of extensions known to withhold expiry dates (such as
.de,.eu, and.ch). When one enters your system, flag itVerification Method: Manual. - Capture proof during setup. When logging into the registrar (GoDaddy, Namecheap, Cloudflare, Gandi, or a local ccTLD registrar), screenshot the billing or renewal page, or copy the renewal date from the invoice into your asset notes.
- Track “Last Verified Date” next to “Expiry Date.” Every manually tracked record should carry both fields. Re-verify after each renewal clears and again at your pre-check milestone (see Section 3). Treat any manual record not verified in the past 12 months as stale.
- Use registrar APIs where you hold the account. For registrars where your agency owns the account, such as Amazon Route 53 (whose
ListDomainscall returns each domain’s expiry and auto-renew flag) or Namecheap (whosedomains.getListcall returns expiry and auto-renew status), account-level APIs return the registrar’s own data and bypass public redactions. Note that this only works for domains inside accounts you control; domains sitting in a client’s personal registrar account still need a manual check.
3. The “Two-Date” Renewal Rule: Separating Vendor Expiry from Client Approval Deadlines
One of the most common mistakes in agency operations is tracking a single date: the Vendor Expiry Date, the day the registrar, host, or certificate authority stops the service.
When your dashboard highlights only that date, urgency anchors to it. If a domain expires on November 30, an alert on November 23 feels like plenty of notice. In an agency-client relationship, seven days is tight.
Why Single-Date Tracking Causes Last-Minute Panic
Between spotting a pending renewal and completing the transaction, several bottlenecks commonly appear:
- Client decision delays: The primary marketing contact leaves, goes on vacation, or needs sign-off from a finance approver who reviews invoices only periodically.
- Payment friction: The card saved in the registrar account has expired, or the charge triggers a bank fraud check requiring the cardholder’s authentication.
- Access gaps: The agency has DNS management access (for example, in Cloudflare) but no billing access to the underlying registrar (for example, Network Solutions), forcing a multi-day account recovery.
- Lifecycle traps: Once a domain expires, what happens next depends on the TLD, and the rules differ more than most teams expect.
What Actually Happens After a Domain Expires
For generic TLDs, ICANN’s Expired Registration Recovery Policy (ERRP) sets a floor:
- Auto-renew grace period: If the registrar does not delete the name at expiration, it may offer a grace period of 1 to 45 days in which the domain can be renewed at the standard price. The length is set by the registrar; some give the full 45 days, many give around 30, and a few give little or none. During this window, many registrars park the domain or suspend DNS and web services even though it can still be renewed.
- Redemption Grace Period (RGP): After deletion, gTLD registries must offer a 30-day RGP in which the registrant can restore the name. Restoration is allowed but typically carries a fee on top of the renewal cost; across registrars, quoted restoration fees commonly run from roughly $70 to $250 or more. A domain in redemption is not active, so the site and email will not work.
- Pending delete: About five days follow before the name is released for anyone to register.
Taken together, the maximum window from expiration to release for a typical gTLD is roughly 80 days, but the useful window, when renewal is cheap and services may still run, is much shorter.
ccTLDs follow their own rules, so do not assume your .com experience applies. The UK registry Nominet, for example, gives a 30-day period to renew after expiry, then suspends the domain for a further period before cancelling it, roughly 90 days after the original expiry, and a suspended .uk domain no longer resolves. DENIC applies a 30-day redemption grace period to .de domains after deletion, but because .de has no public expiry date and deletion can be triggered through the registrar, the practical timeline is far less visible. Always confirm the specific rules for each extension in your portfolio.
Implementing the Two-Date Rule
Separate every renewal lifecycle into two distinct milestones:
- The Client Approval Deadline (T-30 to T-45 days): Your internal operational deadline. By this date the account manager must confirm whether the client wants to keep the asset, verify who is paying, and secure written sign-off or invoice payment.
- The Vendor Expiry Date (T-0): The hard technical cutoff imposed by the registrar or vendor.
Treating the Client Approval Deadline as the primary trigger in your weekly triage builds a 30-to-45-day buffer into the workflow:
| Milestone | Timeline Before Expiry | Owner | Objective |
|---|---|---|---|
| 1. Internal Pre-Check | T-45 days | Ops / Tech Lead | Verify registrar access, check auto-renew status, and confirm current renewal pricing. |
| 2. Client Approval Deadline | T-30 days | Account Manager | Send the renewal notice or invoice; obtain written approval to renew or decommission. |
| 3. Execution & Payment | T-14 days | Ops / Finance | Process the renewal payment, or confirm the client has updated their payment method directly. |
| 4. Final Verification | T-7 days | Ops Lead | Confirm the vendor’s dashboard shows the new future expiration date. |
| 5. Vendor Expiry Date | T-0 | n/a | Hard technical expiration; it should never be reached unrenewed. |
This structure also protects the agency contractually and financially. If a client decides to retire a microsite or campaign domain, finding out at T-30 leaves time to disable auto-renew, archive the site, and avoid an unbillable renewal charge. If a client is unresponsive, you have a documented 30-day trail of outreach before any disruption occurs.
Shorter Certificate Lifetimes Make the Cadence Matter More
The Two-Date Rule applies to SSL/TLS certificates too, and certificate timelines are compressing. Under CA/Browser Forum Ballot SC-081v3, the maximum validity of publicly trusted TLS certificates fell from 398 days to 200 days on March 15, 2026, drops to 100 days on March 15, 2027, and reaches 47 days on March 15, 2029. At 200 days, each public certificate is renewed roughly twice a year; at 100 days, roughly four times; at 47 days, closer to eight. Agencies that rely on manually managed certificates should plan for automated issuance (such as ACME-based renewal) where the hosting platform allows it, and keep an expiry record and an owner for any certificate that cannot be automated. These limits apply to publicly trusted certificates; private PKI certificates used inside a network are outside the CA/Browser Forum rules.
4. Moving Past “Status Unknown”: Standardizing Asset Intake During Post-Launch Handoffs
Even the best triage process struggles if new assets enter your maintenance pipeline with missing data. In many agencies, a chasm exists between the Project Delivery Team (developers, designers, project managers) and the Ongoing Operations/Support Team.
During a launch rush, developers spin up staging environments, buy certificates, connect third-party APIs, and configure DNS. Once the site goes live, the project team moves on to the next build, leaving behind an undocumented web of accounts, credentials, and billing cycles. Months later, the operations team inherits a mystery when an expiration warning arrives.
The Post-Launch Asset Intake Checklist
To keep “Status Unknown” records out of your system, make a standardized asset intake a required gate before a project is marked closed or moved to a retainer. Every handoff should capture five data points for each asset touched during the build:
- Asset identifier and type: Exact domain name, subdomain, hosting environment, SSL certificate, or third-party service (for example, a transactional email provider, maps API, or search index).
- Custody and account location: The vendor or registrar name and the specific account or workspace where the asset lives (for example, Agency Master Cloudflare Account vs. Client-Owned GoDaddy Account).
- Billing responsibility: Who holds the card on file:
Agency Billed & Rebilled,Client Direct Pay, orIncluded in Retainer. - Confirmed expiry date and auto-renew status: Verified directly in the vendor’s billing dashboard on launch day, never guessed.
- Verification method: Whether the asset can be checked through automated RDAP or API lookups or requires a scheduled manual check.
Making Handoffs Frictionless for Delivery Teams
Developers and project managers resist heavy administrative checklists, so integrate intake into existing launch rituals:
- Embed intake in the go-live QA ticket. Add a dedicated section to your launch checklist. If a developer registers a domain or configures DNS during the build, they record the vendor name and expiry date in the ticket while the browser tab is still open.
- Use a standardized form. A simple internal form or database template with dropdowns for
Billing Owner,Registrar, andVerification Typekeeps data clean and consistent. - Hold a 10-minute delivery-to-ops sync. At project close, have the project manager and operations lead review the live asset inventory together. Confirm that credentials are stored in the agency’s password manager, that recovery and notice emails point to a shared agency alias (such as
domains@youragency.com) instead of a departing employee’s inbox, and that the Client Approval Deadline is scheduled in your triage system.
Building a Calm, Predictable Renewal Culture
Reliable renewal operations are less about buying more software than about clear ownership and consistent habits. When an agency pairs a 15-minute weekly triage with the Two-Date Renewal Rule, account managers stop chasing last-minute approvals and finance teams see fewer surprise card declines. By combining automated RDAP and API checks with disciplined manual verification for restricted TLDs, and by enforcing clean metadata capture at every post-launch handoff, you eliminate the “Status Unknown” blind spots that cause outages. Renewals then become a routine background task rather than a recurring client emergency.